Latest post
High zero-day in Citrix NetScaler ADC & Gateway: Patch CVE-2026-88779
A high-severity memory overflow vulnerability was disclosed, affecting Citrix NetScaler ADC and Citrix NetScaler Gateway...
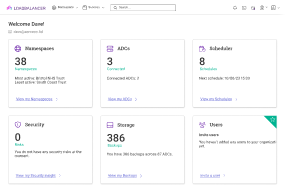
The ADC Portal is a centralized management platform that gives you a single consolidated view of all your load balancers, enhanced visibility and automation capabilities, improved security management, and the ability to organize and effortlessly scale your application delivery infrastructure.
A high-severity memory overflow vulnerability was disclosed, affecting Citrix NetScaler ADC and Citrix NetScaler Gateway...
Tracked as CVE-2026-94127, the flaw carries a near-maximum severity rating and allows unauthenticated remote code execution (RCE)...
A remote code execution vulnerability exists due to improper input validation, which can allow an unauthenticated attacker to execute arbitrary commands...
The question isn't whether another major vendor will suffer a breach — it's whether your infrastructure can survive it...
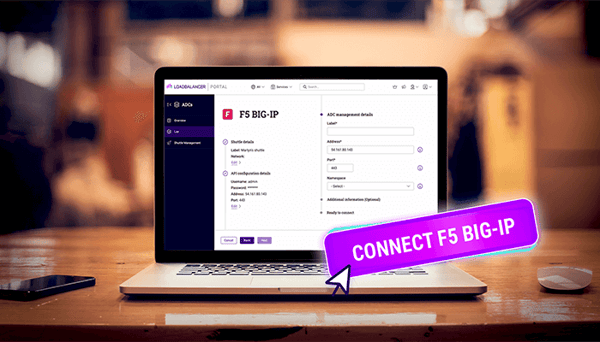
As an F5 engineer, they asked me to test the product and share my honest thoughts...
As a NetScaler specialist, they asked me to test the product and share my honest thoughts...
Note, SAML can only be added by the ADC Portal Admin for your Organization...
If you use HTTPS (SSL or TLS) for your frontend, you must deploy an SSL/TLS certificate on your load balancer to ensure your data remains encrypted...
During the 90-day free trial you can connect multiple ADCs, manage your connected appliances, and get real-time security alerts...
The identification of vulnerabilities can be done in several ways. Here are the methods proposed and supported by F5, and the steps needed to conduct them...
How to stay on top of any NetScaler vulnerabilities to galvanize your network security...
Once the Portal has a correctly configured Shuttle, it is then able to securely communicate with your Kemp...